 TrustView Documentation
2. Citrix NetScaler
2.1. Prerequisites
This integration requires the Automation permission on your TrustView role - read to view a configured Citrix NetScaler instance, write to add, edit or delete one. The built-in roles already have the right access (see the “View/Manage the Automation module” rows under Overview of roles) and can’t be changed - this choice only needs to be made explicitly when defining a custom role.
TrustView has a native integration with Citrix NetScaler. You can connect to any number of Citrix NetScaler instances from TrustView. This will allow you to:
List bound certificates (including expiry dates) for each virtual server
Upload of certificates from TrustView
Binding of certificates available in TrustView to virtual servers
Automated renewal of certificates on Citrix NetScaler
2.2. Adding a Citrix NetScaler instance
Click Citrix NetScaler in the left menu under the Devices section, and fill out the information for the Citrix NetScaler instance.
Important
The user used to access the Citrix NetScaler instance must be Superuser and have CLI and API permissions enabled.
Tip
Superuser is the simplest option to set up, but TrustView only ever calls a narrow set of NetScaler NITRO
API commands - certificate/key management (sslcertkey, sslrsakey, sslecdsakey, sslcertreq),
SSL virtual server bindings (sslvserver, sslvserver_sslcertkey_binding), SSL profiles (read-only) and,
if partitions are used, nspartition. It never touches networking, vserver creation or anything outside SSL
certificate management. A custom NetScaler command policy scoped to just those command groups (plus
login/logout) is likely sufficient for a more restricted account, for environments that want to avoid
granting Superuser.
Important
The certificate on the Citrix NetScaler web interface must be valid and trusted by TrustView in order to connect to the Citrix NetScaler instance from TrustView.
If the certificate is internally issued by your CA, the simplest way to establish trust is to add it under
Manage trusted certificates, which takes effect immediately. Alternatively, it can be
added to the Java keystore (cacerts file) as described here, which requires a
Tomcat restart. See Diagnosing certificate trust errors for commands
to see exactly which certificate is missing.
Note
TrustView connects to NetScaler over its native NITRO REST API (/nitro/v1/config/... endpoints), the same
API NetScaler’s own management tools use.
Click Add to create the Citrix NetScaler instance.
Note
TrustView has no awareness of NetScaler HA pairs or clusters - it only ever talks to the single hostname/IP configured here. Point it at the HA pair’s shared management address (the one that always reaches the current primary node), not a node’s own private address, and let NetScaler’s own HA configuration sync propagate the change to the secondary node - TrustView never connects to the secondary directly.
2.3. Admin Partitions
If the connected Citrix NetScaler instance has more than one Admin Partition configured, a Choose partition
dropdown appears on the instance’s edit page. Selecting a partition scopes the rest of the page - virtual server
listing, certificate binding/removal, certificate upload, and automation agent setup - to that partition. An
instance with only one partition (the default) does not show this dropdown.
2.4. Virtual servers
We support all the virtual server types from Citrix NetScaler and enable you to add new certificates to the virtual servers and remove the bindings directly from TrustView.
The virtual servers must be added to your Citrix NetScaler first, and then they will be added to the list under the Virtual servers section in TrustView automatically.
The certificates (if any) listed in the subtables are retrieved from the virtual servers on the Citrix NetScaler instance. Each certificate on the list can have its binding removed by clicking the button on the right of the certificate:

You can check the current bindings of a specific certificate in the Certificates section below Virtual servers.
2.5. Add a certificate to the virtual server
Important
To allow for uploading of certificates from TrustView, SSH must be enabled (port 22 must be open).
Select one or multiple virtual servers from the list and click Add certificate. A modal will prompt you to select a certificate from the list of available certificates.
Enable SNI (Server Name Indication) for the certificate by checking the checkbox before adding the certificate.
Read more about Server Name Indication.
2.6. Certificates
2.6.1. Update certificate
To update a certificate click Update certificate and a list of the available certificates stored in TrustView will be shown.
Note
The certificates must be issued, have a private key, be Active in TrustView and not be expired, to be valid and shown on the list.
2.6.2. Configure automation for certificates
To configure automation for the certificate click the Automation agent details button to the right of the certificate.
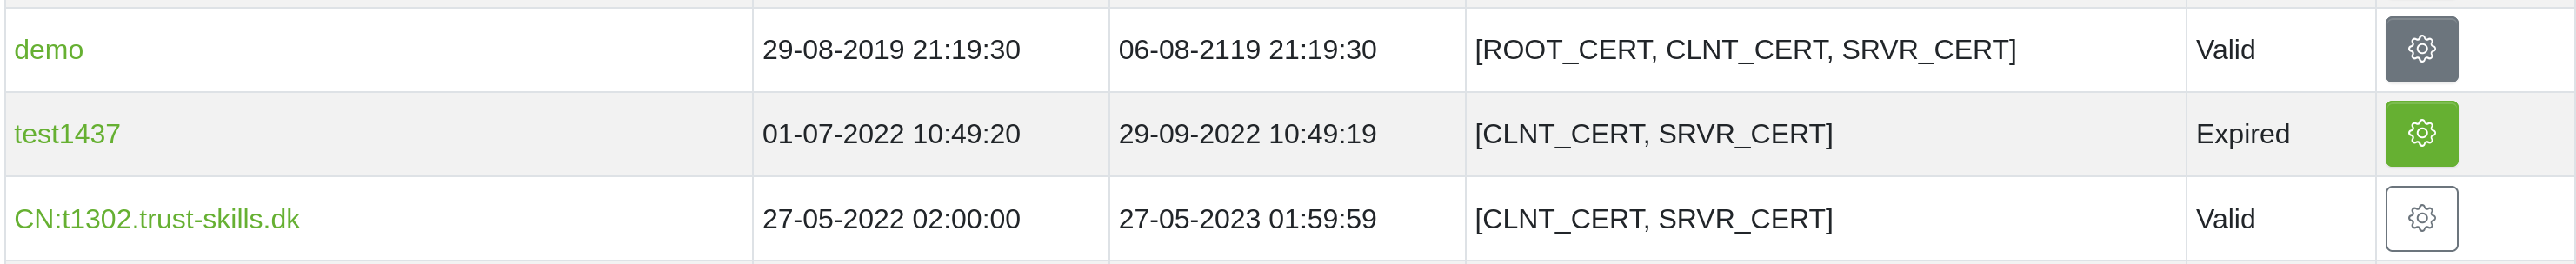
The button on the Citrix NetScaler overview page only distinguishes two of the automation states directly: it is shown in a gray state when the automation agent is Ignored, and in a green state when it is Active. In every other case - including when automation has never been configured, and when it is Error, Disabled or awaiting approval - the button is shown in the same white/outline state, so a failed or disabled automation looks identical to one that was never set up.
Tip
If a certificate you expect to be automated isn’t showing green, click Automation agent details and check the automation function’s actual status rather than relying on the button’s color alone.
2.6.3. Requirements for automation
See the requirements for automation with Citrix NetScaler certificates here.